Microsegmentation
East-west and north-south traffic segmentation.
Cybersecurity
We design environments with logical, physical and virtual protection layers, traffic visibility, advanced segmentation and fault tolerance.
Assess a security architecture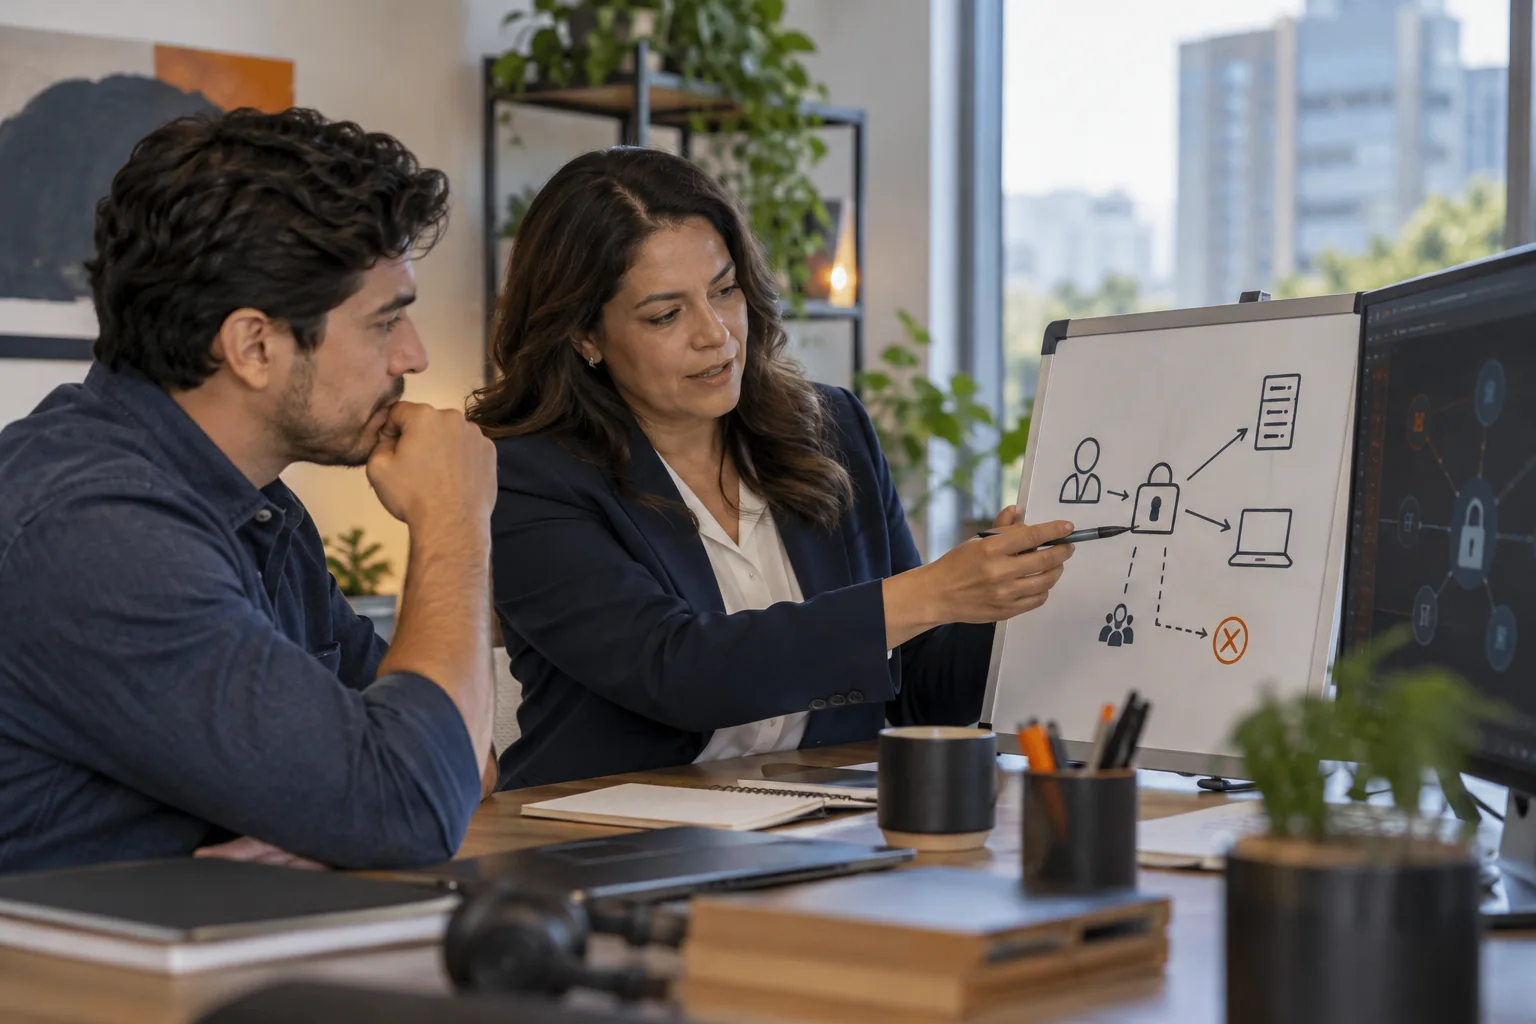
Solutions and scope
Protection should not be added at the end. It must be part of the architecture, access policies and how the system detects, contains and responds to events.
East-west and north-south traffic segmentation.
Intent- and risk-profile-based access.
Physical and virtual controls integrated into SDN traffic flows.
Continuous observation and incident-response readiness.
Automated isolation policies triggered by events.
Design for fault-tolerant distributed environments.
From need to scope
For organizations that need to segment environments, review access and reduce exposure of systems that sustain operations.
Priority assets, access, network segments and existing policies. Do not send passwords, private keys or vulnerability details through the form.
Final scope, timelines and support terms are agreed in a proposal before work begins.
Define my projectBefore we begin
Any active test requires specific scope and authorization. The initial discussion defines objectives and limits; it does not grant permission to intervene in your systems.
This page describes architecture and integration services. Coverage, hours, support and service agreements are specified in writing in each proposal.
Enterprise perspective